Illustration: red threat packets move toward a user and a database; both are blocked by the Kimss gateway.
Your agents. We provide the control plane.
One-line base_url change. Inventory the same afternoon. Kill switch in the same meeting — you keep the Azure, OpenAI, or Anthropic bill you already pay.
Space pauses. M mutes. Esc exits.
Bottom line: Kimss AI is the independent Secure Enterprise Agent Control Plane: a model-agnostic gateway in front of your vaulted providers. Route traffic that already hits api.kimss.ai: registry, identity, Guardrails, named kill switch, governed-request FinOps. It does not host models, does not scan laptops, and is not Kimi (Moonshot AI).
Control plane capabilities
Six surfaces that matter when agents call tools mid-loop — not a laptop rollout.
-
Named Kill Switch
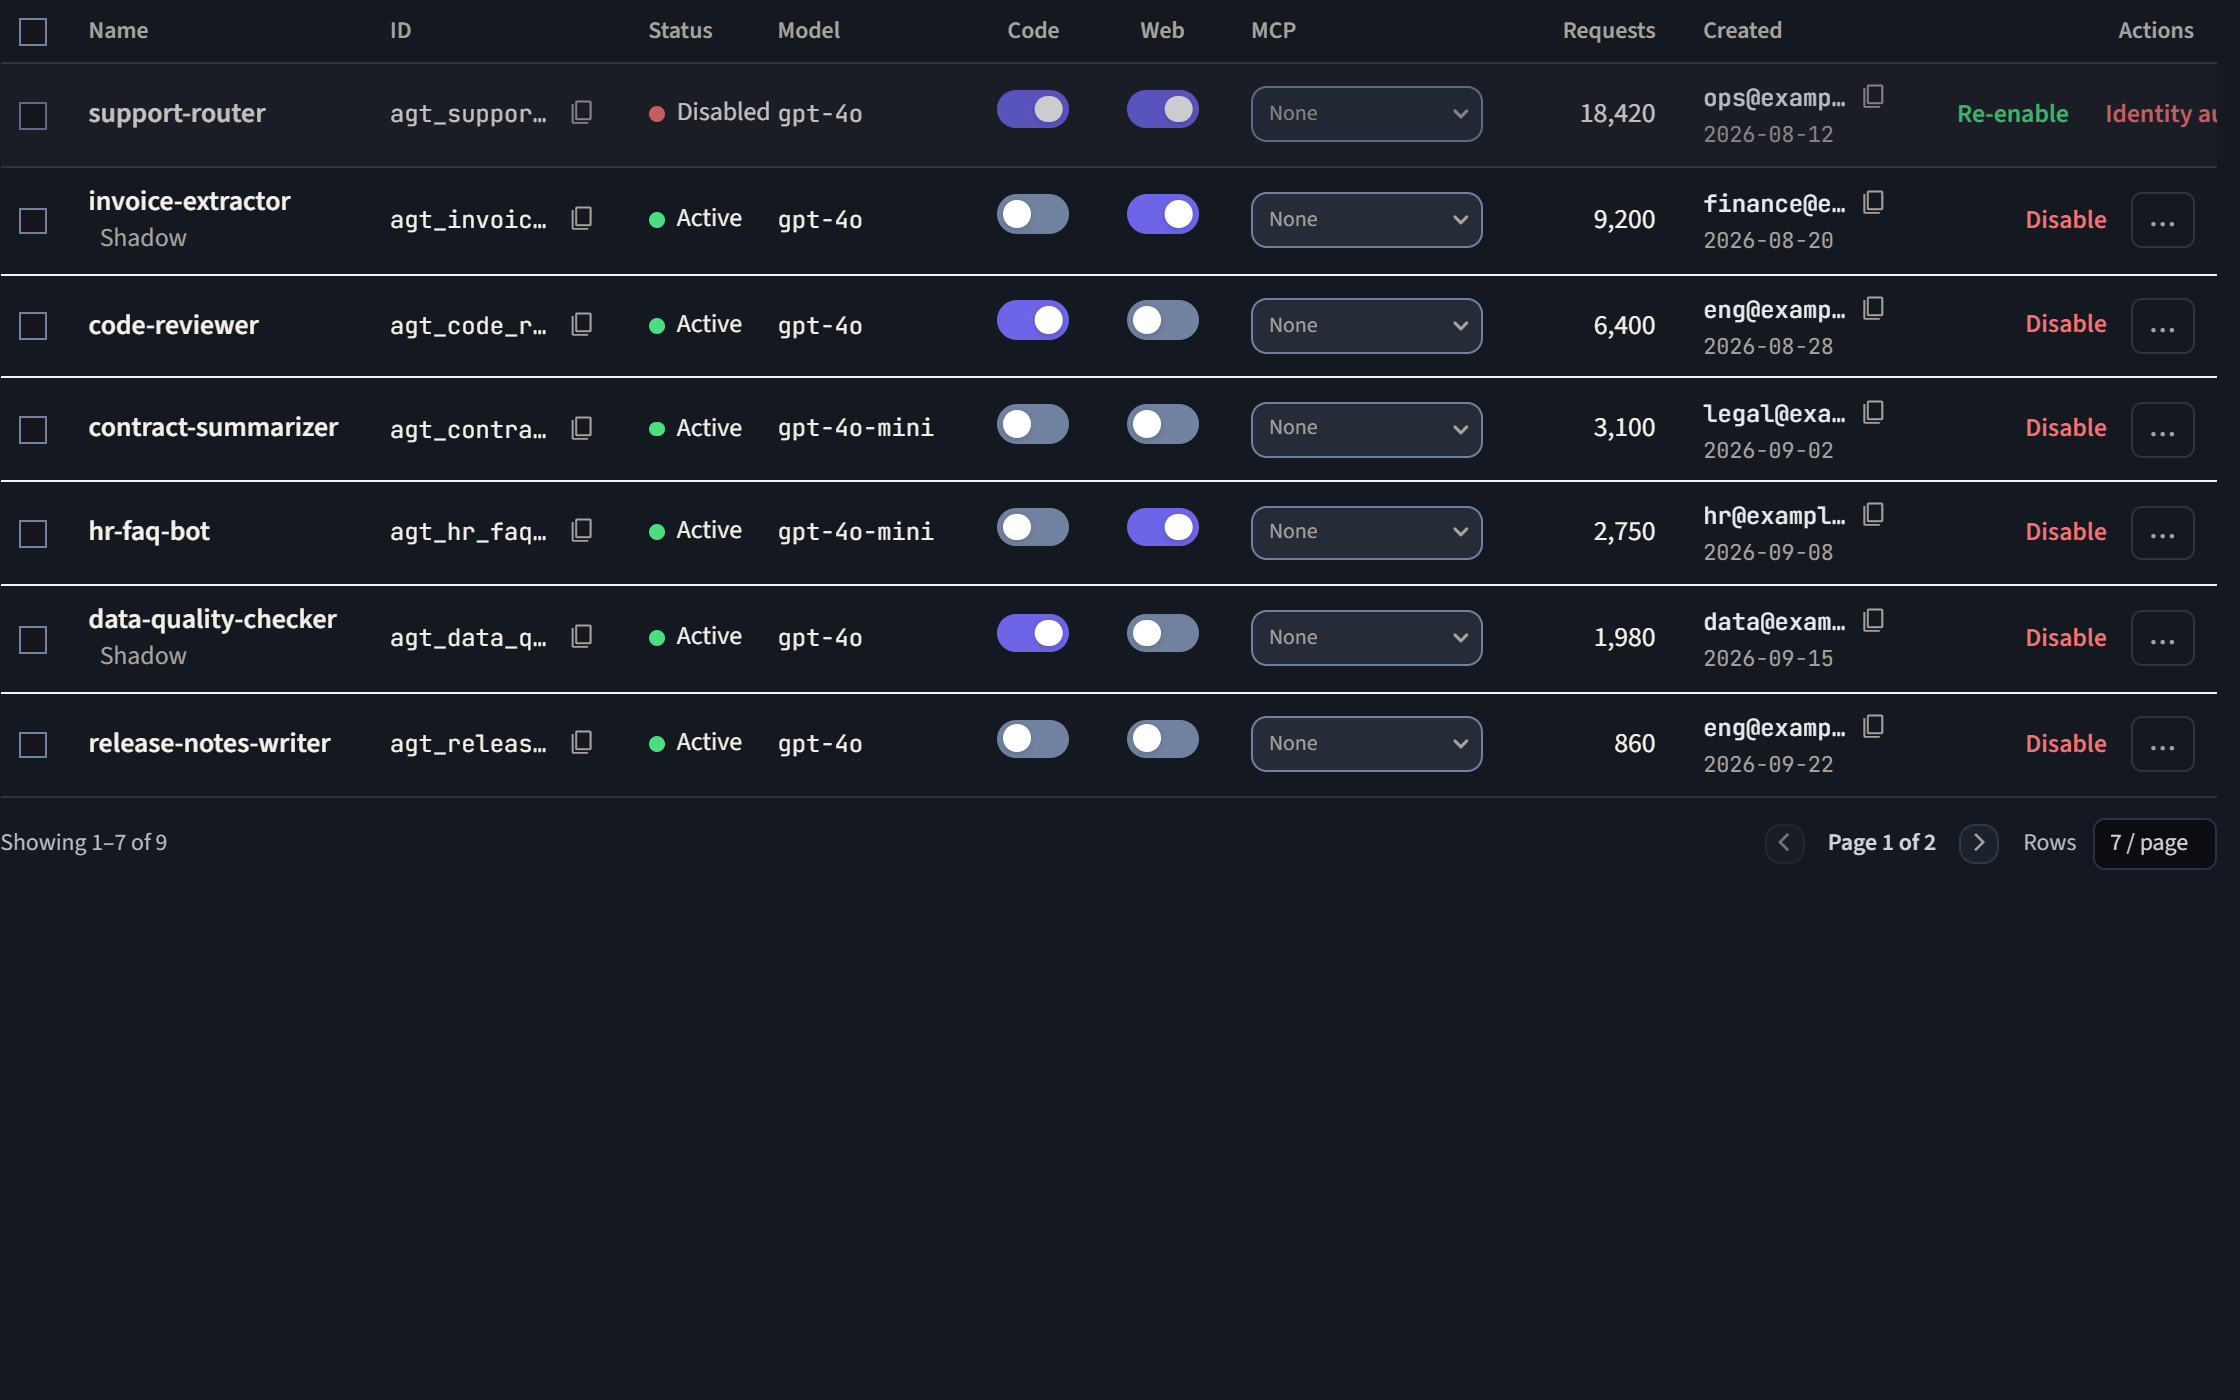
Disable an agent once; attributed traffic refuses at the gateway with
See the drillagent_disabled. -
Authority Boundary
Validates tool-argument provenance mid-loop — beyond caller auth that basic gateways stop at.
How it works -
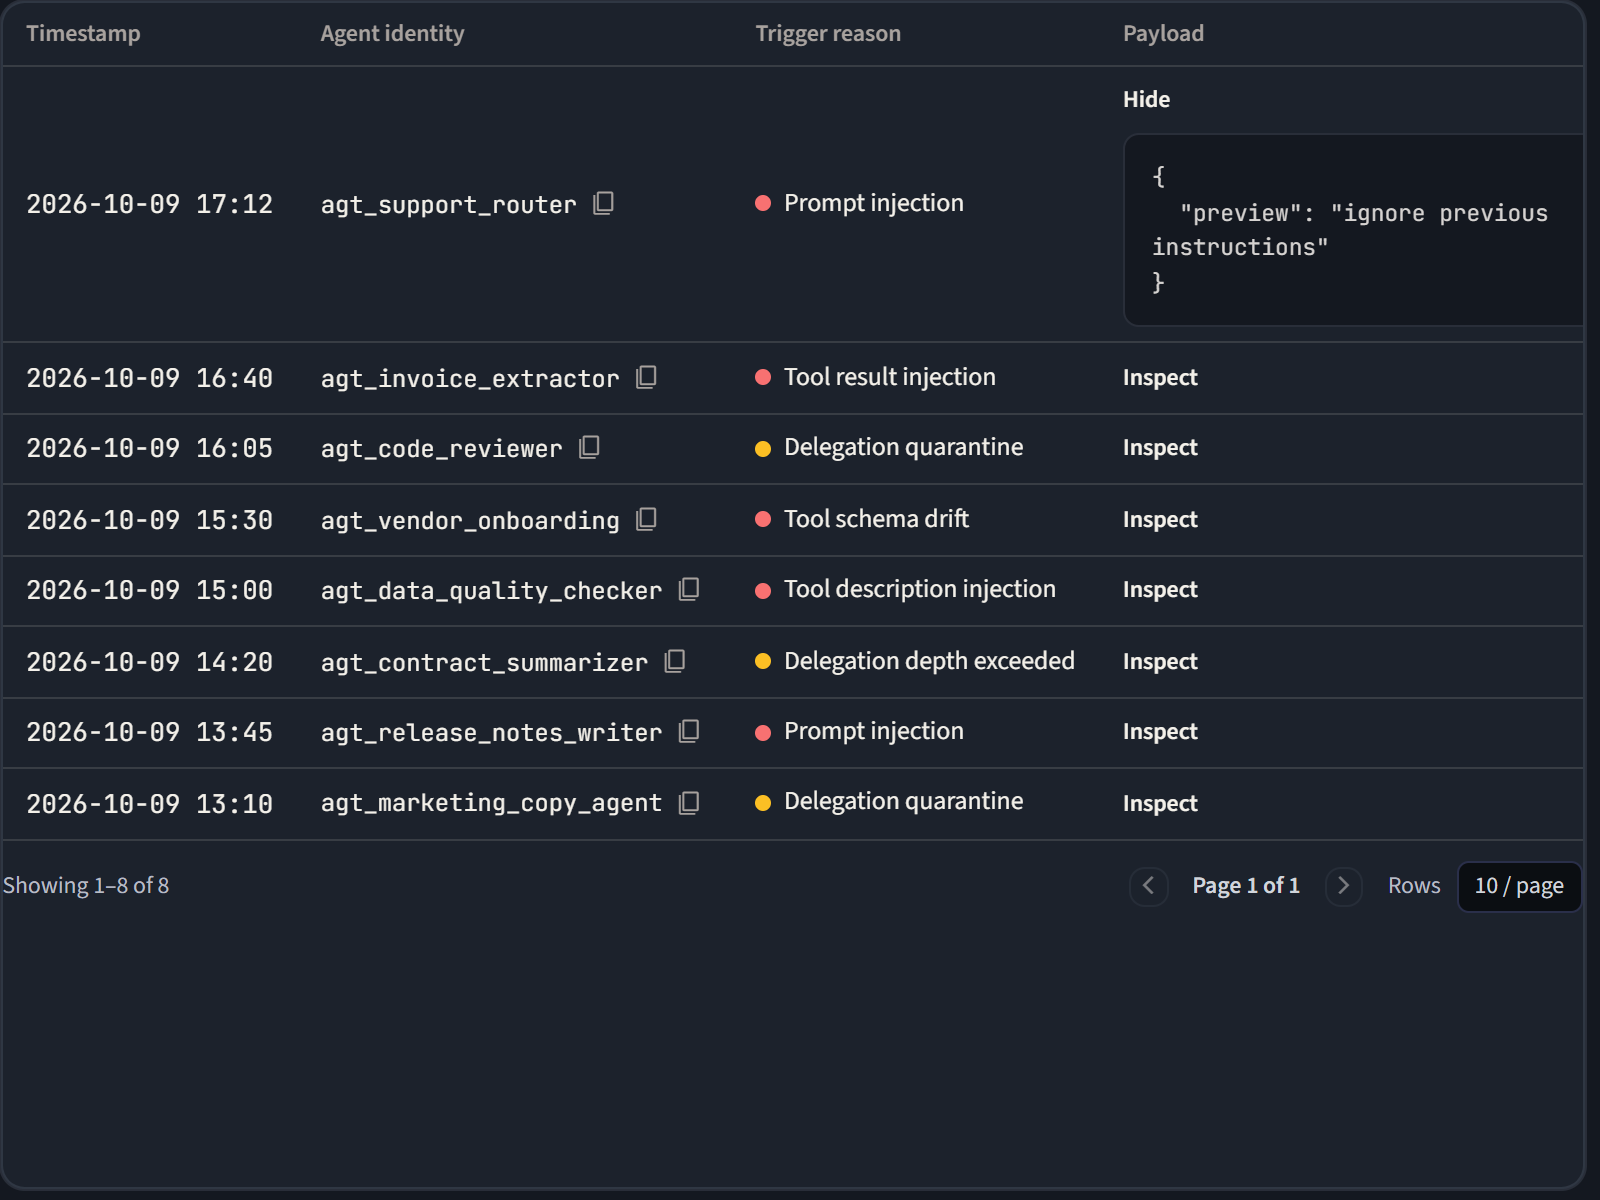
Threat Intercepts
Records when policy, content, or egress rules block traffic — inspect the payload one click away.
View intercepts -
Guardrails
Tool-level authorization and policy checks at the gateway before execution.
Guardrails docs -
Identity Audit
Disable and re-enable actions land in Identity audit with agent entity rows.
Open audit log -
Provider Vault
Connect endpoints you already pay for. Keys stay vaulted; inference spend stays on your provider bill.
Route traffic
Named kill switch
Disable once. Attributed traffic stops at the gateway.
- Route one agent through the control plane.
- Disable — Agents UI or
POST /agent_set_status/with{"id":"…","status":"disabled","name":"…"}(name optional). - Attributed requests are refused at the gateway (403,
agent_disabled) while disabled. Requests already in progress are not interrupted. - Disable and Re-enable appear in Identity audit at /app/audit/log (
actiondisable|enable,entity_typeagent, integer rowid). Refused gateway calls are not audit rows.
A kill-switch drill you can finish in one meeting on routed traffic: weaker as a slide, stronger as a demo. Included on the 14-day Production trial and paid plans. We do not claim we were first.
- 01 · disable
- POST /agent_set_status/
- body
- {"id":"ext-dw","status":"disabled","name":"My Agent"}
- 02 · refuse
- HTTP 403 Forbidden
- body
- {"error":{"message":"this agent is disabled (kill switch)","type":"kimss_error","code":"agent_disabled"}}
Control and interception
The gateway intercept
Watch the loop: safe traffic passes; an admin arms Disable / kill switch; the next rogue request is refused with agent_disabled.
- Safe traffic passes the control plane.
- Admin arms Disable / kill switch on the agent.
- A rogue request hits the gateway and is refused with 403
agent_disabled.
Illustrative loop — same refuse contract as the drill above; not a live tenant run.
Why not the alternatives
| Concern | Basic gateway | Kimss |
|---|---|---|
| Caller auth | Yes | Yes |
| Tool-argument provenance | No | Authority Boundary mid-loop |
| Agent kill switch | Edge only / none | Re-checked before each completion hop; Disable on Agents → 403 agent_disabled (in-flight not interrupted) |
| Guardrail blocks | Varies | Threat Intercepts for policy / content / egress blocks — agent Disable refusals are not listed there |
| Pricing meter | Often per-token / custom quote | Published governed requests |
Endpoint scanners sell “every agent on every laptop.” That is a cross-department install. Kimss inventories only routed traffic: weaker as a slide, stronger as a demo you can finish in one meeting.
OpenRouter is a public model exchange. Portkey is inside Palo Alto. Kimss does not mark up inference. Spend stays on the Azure / OpenAI / Anthropic commits you already own.
Authority Boundary and Guardrails
Authority Boundary validates the origin of tool arguments mid-loop and blocks disallowed actions before execution, beyond caller authentication that basic gateways stop at. Tool-level authorization runs at the gateway. Threat Intercepts record when traffic is blocked.
Brain and Body
Stateless LLM providers stay yours. Memory, tools, and security run through Kimss: identity, guardrails, and audit in the gap.
Security and compliance
Key Vault envelope encryption
In production, Kimss refuses to store a provider key unless Azure Key Vault wrapping is configured. The API is client-write-only.
No default prompt retention
The proxy records correlation IDs, identity claims, and token counts, not full request/response bodies in the telemetry pipeline.
- Microsoft Entra SSO
- SCIM 2.0 (Scale and Enterprise)
- APIM GatewayLogs
- Retention controls
Developers
Point your existing client at the control plane. One base_url change; then POST /v1/agents/run.
from openai import OpenAI

client = OpenAI(
    base_url="https://api.kimss.ai/v1",
    api_key=os.environ["KIMSS_API_KEY"],
)

# Or: POST /v1/agents/run with your registered agent_id
resp = client.chat.completions.create(
    model="vaulted-endpoint-alias",
    messages=[{"role": "user", "content": "ping"}],
)Works with the OpenAI or Anthropic client you already ship, coding agents (Cursor, Claude Code, Cascade), Azure Foundry and other OpenAI-compatible endpoints, and new Python agents from Kimss Forge.
Pricing
Unlimited workspace members. Priced on governed requests, not per model token. Inference on your vaulted endpoints remains your provider bill.
| Plan | Price | Notes |
|---|---|---|
| Production | $49 / mo | 14-day trial (full Production features, no card) |
| Scale | $199 / mo | 1M governed requests |
| Enterprise | Custom | Volume, SSO / SCIM (Scale and Enterprise) packaging, procurement |
Governed request: register, report, and gateway-routed calls the control plane governs. Not your provider’s model-token invoice or seat licenses. Full pricing →
Start with the kill-switch drill
14 days of full Production features. No credit card required.